
Atlassian pulls the plug: Jira Data Center is being phased out – we’ll guide your journey into the future
Atlassian has announced it will phase out Jira Data Center. Hardly a surprise, but it calls for a clear response. The clock is ticking: as of 28. März 2029, Jira Data Center will be available in read-only mode. From März 2026, no new licenses will be available, and from März 2028 the option to extend […]

Audits and regular reviews: How an ISMS is continuously improved
An ISMS is not a project – It is a process The information security management system (ISMS) is already implemented in many companies or in the process of being introduced. But even with a cleanly documented system, up-to-date policies, and a completed audit, the work is not done. On the contrary: An ISMS that is […]

Audits and Regular Reviews: How ISMS Is Continuously Improved
ISMS is not a project. It is a process. The information security management system (ISMS) has already been implemented in many companies or is in the process of being introduced. But even with a cleanly documented system, up-to-date policies, and a completed audit, the work is not done. On the contrary: an ISMS that is […]
ProForma: Forms & Custom Fields for Jira
What is ProForma in Jira Service Management Data Center? How the integrated forms work The news that Jira Service Management Data Center integrates ProForma for free with version 10 changes the way forms are conceived within the platform. What used to be a paid plugin is now available to every company that uses Jira Service […]
ISMS for Small Businesses: Practical Tips for Implementation and Cost Control
An information security management system changes how you view processes. It sharpens the questions of who has access to what, which systems are critical, which workflows are documented—and which are not. In large corporations, dedicated departments are created for this. Small companies often lack the capacity. The risk, however, remains the same. Data loss is […]
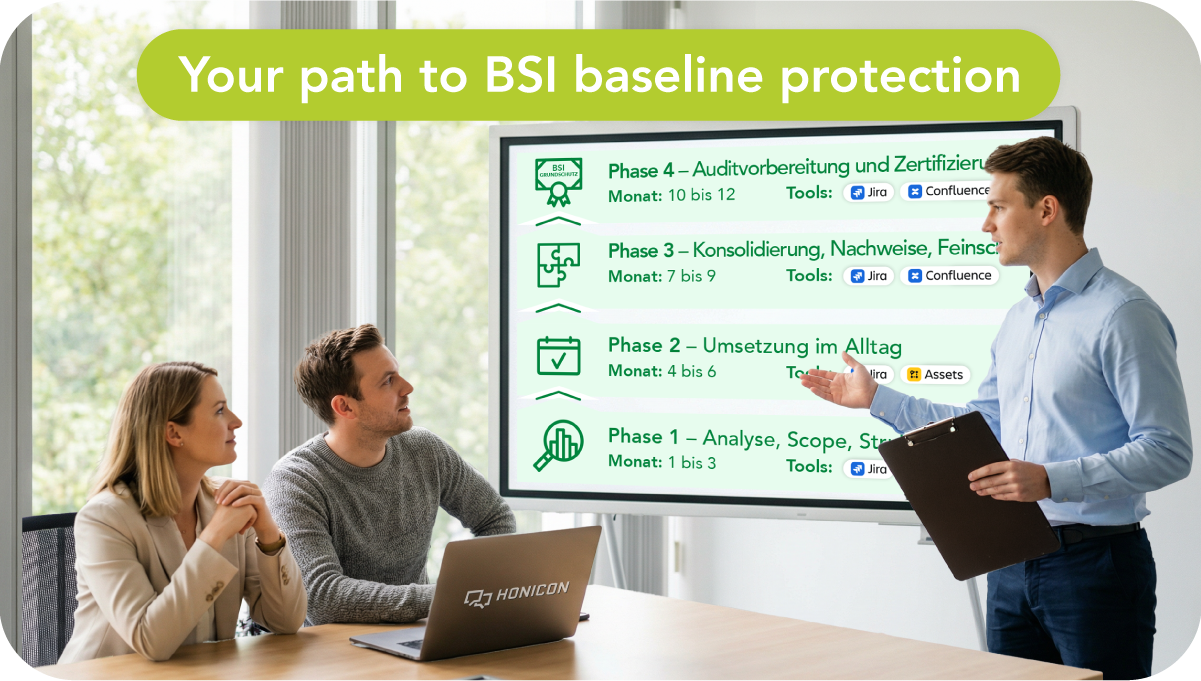
From Initial Consultation to Certification: Your Path to BSI IT-Grundschutz
ℹ️ tl;dr Initial assessment based on BSI IT-Grundschutz: Scope, relevant modules, and the target certification level are clearly defined. Jira as a control instrument: Requirements, risks, and measures are brought together – with transparent responsibilities, deadlines, and workflows. Confluence as an evidence base: Policies, logs, and documentation are bundled in an audit-proof manner and linked […]
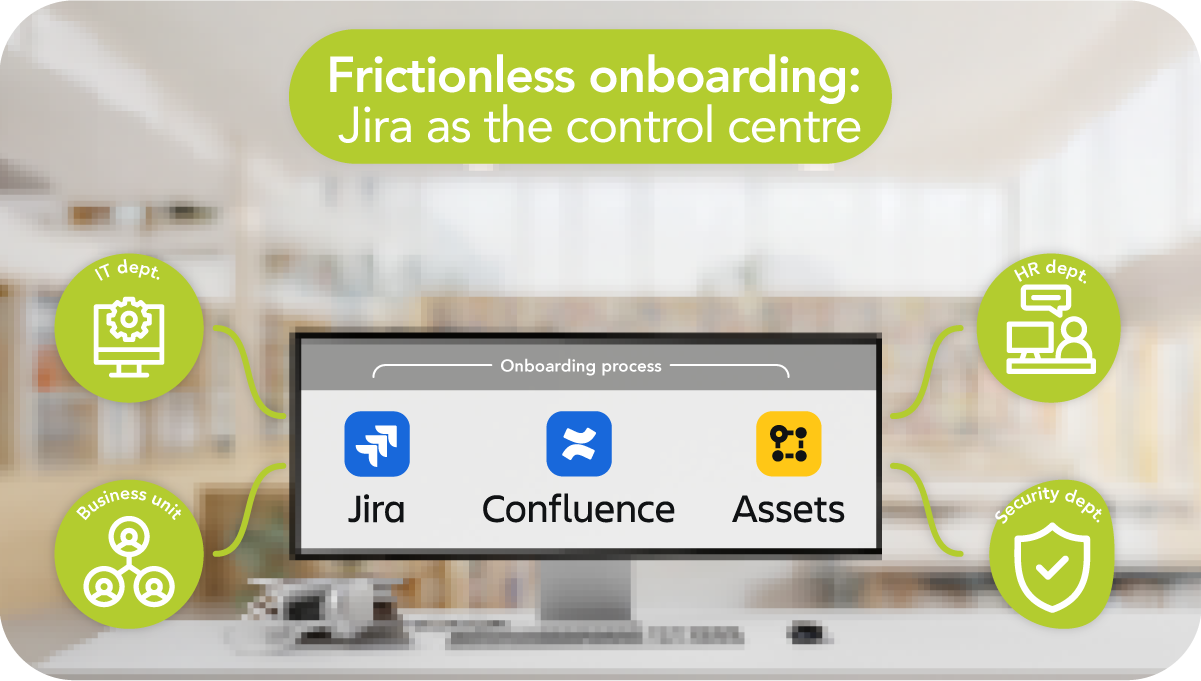
Frictionless onboarding: Jira as the control center
ℹ️ tl;dr Jira bundles onboarding end to end: one issue instead of scattered emails and lists, clear rules, deadlines, statuses, and automatic follow-up tasks. Change processes follow the same logic: approvals along defined responsibilities, permission changes, and handovers as traceable task packages. Assets embedded directly in the process: assignment of work equipment via Jira Assets, […]
BSI Standard 200-4: Business Continuity Management in the Public Sector
ℹ️ tl;dr BSI Standard 200-4 describes Business Continuity Management as a management responsibility and is aligned with ISO 22301:2019 for organizational resilience. The Business Impact Analysis (BIA) identifies critical processes, dependencies, and recovery times as the basis for emergency plans and crisis organization. Honicon integrates BCM directly into digitized end-to-end processes instead of isolated specialist […]
BSI Baseline Protection for Public Administration
ℹ️ tl;dr BSI Baseline Protection provides the framework for legally compliant information security in authorities – from federal agencies to municipal administrations. The IT Baseline Protection Compendium with 111 modules structures management tasks, organizational rules, and technical safeguards across ten layers. Honicon’s 4-step method connects BSI Baseline Protection with Atlassian tools: Analysis → Concept → […]
BSI Standard 200-1: Lead, govern, and demonstrate information security
ℹ️ tl;dr BSI-Standard 200-1 prioritizes systematic management over individual measures and anchors information security as a leadership responsibility. The executive level decides on risks, resources, and information security objectives and ensures integration into existing structures. Honicon designs processes so that the requirements of BSI Standard 200-1, ISO standards, and legal obligations are met, and an […]