
We Need to Talk About Data Protection, Atlassian!
Starting August 17, 2026, Atlassian is changing its data processing. As an Atlassian partner, we say: We need to address this. ℹ️ tl;dr Starting August 17, 2026, Atlassian will use customer data for AI training. Approximately 300,000 companies worldwide are affected – those who do not actively object are included automatically. In-app data can be […]
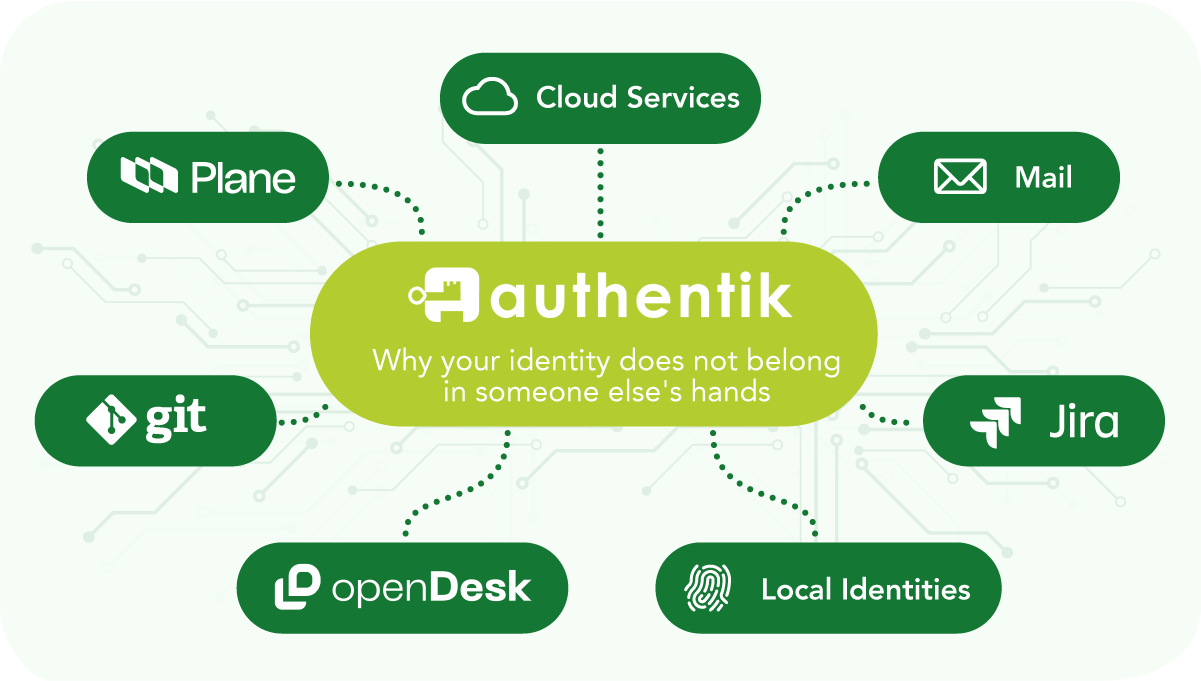
Authentik: Why Your Identity Doesn’t Belong in Someone Else’s Hands
There are systems you can ‘quickly’ outsource. And there are systems that are something like the backbone of your entire digital infrastructure. Identities and permissions clearly belong to the second category for me. If your identity provider (IdP) wobbles, everything wobbles: VPN, email, Git, Kubernetes, Atlassian, HR tools, password manager, cloud console—and, in case of […]

Audits and regular reviews: How an ISMS is continuously improved
An ISMS is not a project – It is a process The information security management system (ISMS) is already implemented in many companies or in the process of being introduced. But even with a cleanly documented system, up-to-date policies, and a completed audit, the work is not done. On the contrary: An ISMS that is […]
NIS2 is coming – are you ready?
Many companies that previously did not consider themselves “critical” are suddenly in the spotlight of European cybersecurity regulation. IT management, executive leadership and security officers in medium-sized companies are currently asking: Are we affected by the NIS-2 Directive – and what exactly does that mean for us? On 30. Juli 2025, the Federal Office for […]

Critical Security Vulnerability in Microsoft SharePoint: Urgent Action Required for Businesses!
“The on-premises instances of Microsoft SharePoint are currently threatened by highly critical security vulnerabilities. This means action is required. Some of these vulnerabilities are already being actively exploited.” Claudia Plattner, President of the BSI Video message from the BSI In a recent video message, the Federal Office for Information Security (BSI) issues an urgent warning about a […]

Digitalization in public administration: opportunities, challenges, and how Honicon GmbH’s Cyber Security Check helps
A conversation among equals: What digitalization in public administration means today The digitalization of public administration is a central topic for public authorities and companies alike. As part of a recent conversation between Helene Brubrowski and Claudia Plattner, a renowned expert in public-sector digitalization, it became clear: The biggest challenges lie not only in outdated […]
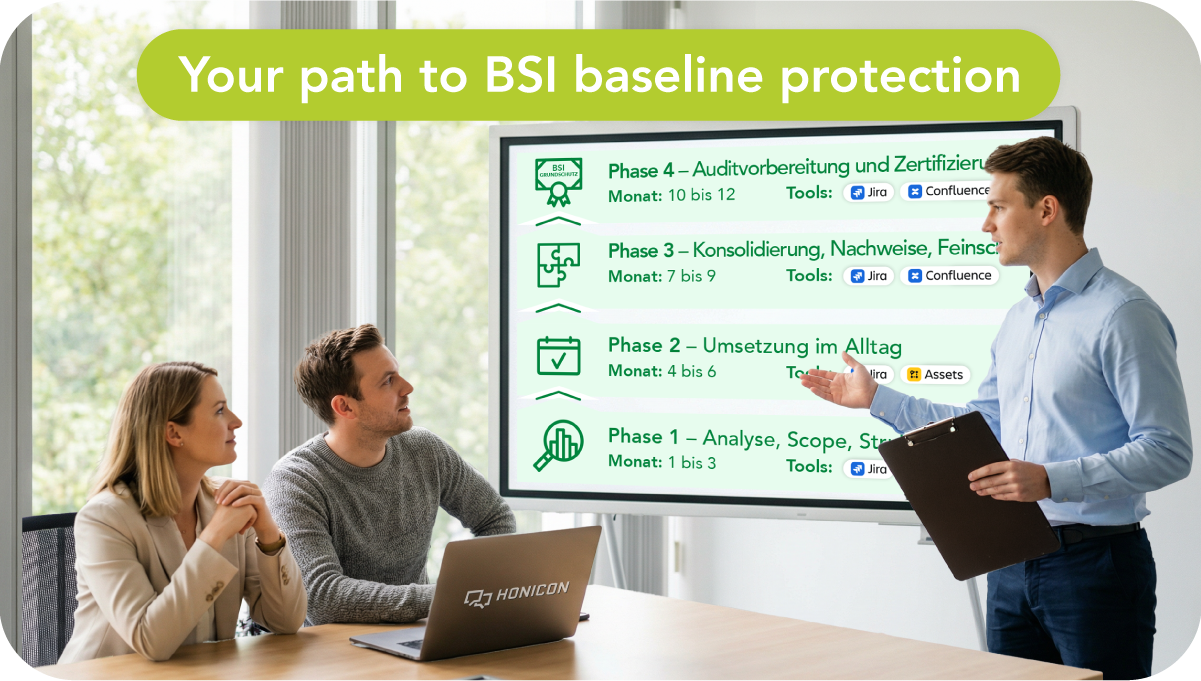
From Initial Consultation to Certification: Your Path to BSI IT-Grundschutz
ℹ️ tl;dr Initial assessment based on BSI IT-Grundschutz: Scope, relevant modules, and the target certification level are clearly defined. Jira as a control instrument: Requirements, risks, and measures are brought together – with transparent responsibilities, deadlines, and workflows. Confluence as an evidence base: Policies, logs, and documentation are bundled in an audit-proof manner and linked […]
BSI Standard 200-4: Business Continuity Management in the Public Sector
ℹ️ tl;dr BSI Standard 200-4 describes Business Continuity Management as a management responsibility and is aligned with ISO 22301:2019 for organizational resilience. The Business Impact Analysis (BIA) identifies critical processes, dependencies, and recovery times as the basis for emergency plans and crisis organization. Honicon integrates BCM directly into digitized end-to-end processes instead of isolated specialist […]
BSI Baseline Protection for Public Administration
ℹ️ tl;dr BSI Baseline Protection provides the framework for legally compliant information security in authorities – from federal agencies to municipal administrations. The IT Baseline Protection Compendium with 111 modules structures management tasks, organizational rules, and technical safeguards across ten layers. Honicon’s 4-step method connects BSI Baseline Protection with Atlassian tools: Analysis → Concept → […]
BSI Standard 200-1: Lead, govern, and demonstrate information security
ℹ️ tl;dr BSI-Standard 200-1 prioritizes systematic management over individual measures and anchors information security as a leadership responsibility. The executive level decides on risks, resources, and information security objectives and ensures integration into existing structures. Honicon designs processes so that the requirements of BSI Standard 200-1, ISO standards, and legal obligations are met, and an […]